
A cybersecurity awareness program that runs on a schedule, not on hope.
Five components, each on its own cadence, working together year-round so awareness does not lapse between audits.
Awareness that does not lapse between audits
Most awareness training is a once-a-year video and a spreadsheet of completions. It satisfies the box on the insurance form and changes almost nothing, because awareness decays and the calendar does not remind anyone.
Five components, one program.
Each runs on its own cadence. Together they cover the whole year, not just the week of the annual training.
A full curriculum covering current threat vectors, password hygiene, credential security, and safe use of AI tools at work. Every employee completes it once a year, so the baseline never goes stale.
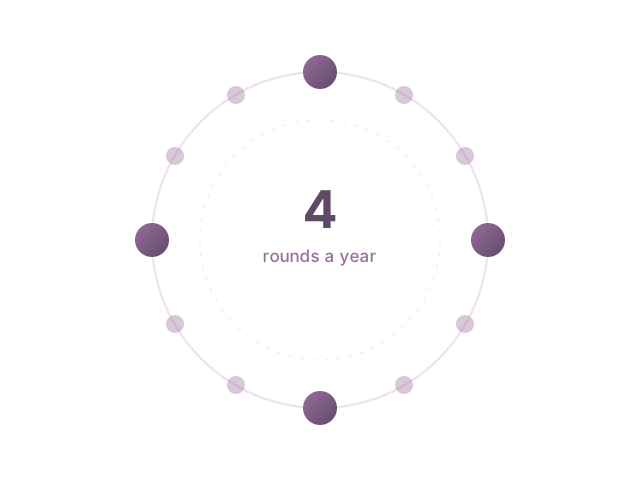
Controlled, realistic phishing and social engineering campaigns four times a year. Each round measures who clicks, who reports, and how fast — and feeds directly into the next round of training.
Cybersecurity orientation built into account provisioning. Every incoming employee finishes the fundamentals before their first login, rather than waiting for the next scheduled training cycle.
A short, actionable tip lands every month to keep security top of mind between formal trainings. At year end it rolls up into a compliance report and certificate suitable for a cyber insurance audit.
Plain-language updates for ownership: dark web monitoring findings and Microsoft Secure Score posture, reviewed monthly with a fuller executive summary each quarter.
This is what a round actually looks like.
One of the simulations from the library — the same thing your team sees, four times a year.
How the year runs
We confirm scope and headcount, then schedule your first training cycle. The first phishing simulation runs within 30 days.
The full curriculum goes out to every employee once a year — threat vectors, password hygiene, credential security, and safe use of AI at work.
Four controlled campaigns, rotating difficulty. Results land within five business days and shape the next round.
A short tip on the first business day of each month, plus a Secure Score review and dark web monitoring findings for ownership.
A completion and performance report for your records, and a certificate formatted for a cyber insurance audit.
Straightforward per-user pricing
- • Minimum 10 users
- • Annual training curriculum
- • Quarterly phishing simulations
- • New hire onboarding modules
- • Monthly tips by email
- • Annual compliance report
- • Minimum 10 users
- • Everything in Essentials
- • Dark web monitoring
- • Monthly Secure Score review
- • Quarterly executive summary
- • Cyber insurance audit certificate
- • Starting at 50+ users, multi-site
- • Everything in Business
- • Custom curriculum branding
- • Department-level phishing analytics
- • Dedicated program manager
- • Quarterly on-site or live review
Four rounds a year, not one video
Every quarter rotates through easy, medium and hard pretexts. A new hire is onboarded within 24 hours of their account being created, not at the next annual cycle.
Request a proposal
Tell us your headcount and we will match a tier to it — and send the free assessment either way.